Imagine this: you spend months building a customer database, only to realize half your team has been emailing sensitive health records through personal Gmail accounts. Or worse, you just got hit with a £17.5 million fine because someone forgot to delete old user data. This isn't hypothetical-it happens every week. Compliance training is the bridge between doing business and getting sued, but most companies treat it like a boring checkbox exercise that nobody actually remembers.
If you’re running a business in 2026, whether you’re based in Edinburgh or anywhere else in the UK, you’re likely juggling at least two major regulatory frameworks. Maybe it’s the General Data Protection Regulation (GDPR), which governs how you handle personal data across Europe. Or perhaps you’re dealing with HIPAA (Health Insurance Portability and Accountability Act), especially if you have US clients or partners in healthcare. These aren’t just legal hurdles; they’re operational realities. The question isn’t whether you need training-it’s how to make it stick without turning your staff into zombies who click "Next" until the video ends.
Why Generic Training Fails Every Time
Here’s the hard truth: most compliance training fails because it’s generic. You buy a package from a big vendor, it covers everything from cybersecurity basics to anti-bribery laws, and it takes four hours to complete. Your employees hate it. They learn nothing. When an auditor comes knocking, you can show them the completion certificates, but when a data breach actually happens, those certificates won’t save you.
The problem is relevance. A marketing intern in London doesn’t need the same depth of knowledge about medical record encryption as a nurse practitioner in Manchester. Yet, both often get the same module. Effective compliance training must be role-specific. If you’re handling patient data under HIPAA, you need to know exactly what constitutes Protected Health Information (PHI). If you’re managing customer emails under GDPR, you need to understand consent withdrawal mechanisms. Mixing these up creates confusion, and confusion leads to mistakes.
Think about the last time you tried to learn something new. Did you remember the 45-minute lecture on abstract principles? Probably not. But did you remember the specific instruction on how to lock the front door before leaving? Absolutely. That’s contextual learning. Your training needs to mirror real-world scenarios your team faces daily, not theoretical edge cases that happen once a decade.
Decoding GDPR vs. HIPAA: Know Your Boundaries
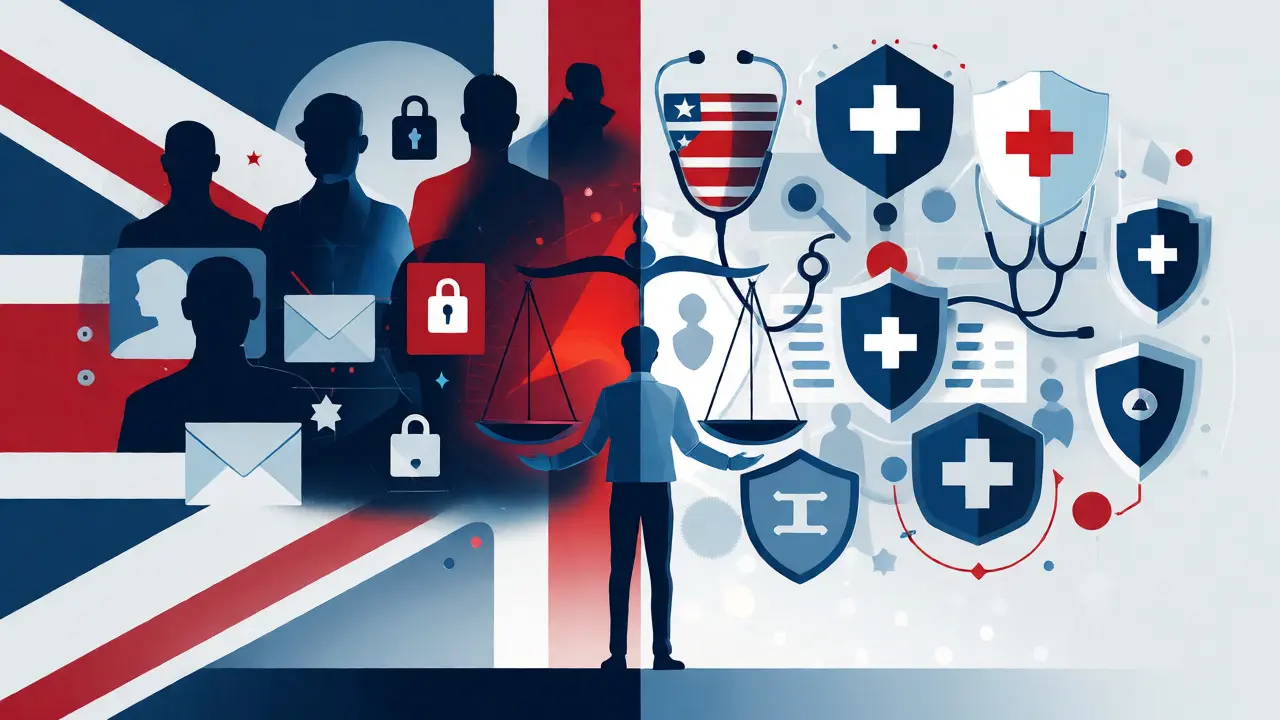
Let’s clear up the biggest misconception right now: GDPR and HIPAA are not interchangeable. While they share the goal of protecting data, their scope, enforcement, and penalties differ significantly. Understanding these differences is crucial for designing effective training modules.
GDPR applies to any organization processing the personal data of individuals within the European Union and the European Economic Area, regardless of where the company is located. It focuses on broad categories of personal data-names, email addresses, IP addresses, location data-and emphasizes individual rights like access, rectification, and erasure. Penalties can reach up to 4% of global annual turnover or €20 million, whichever is higher.
HIPAA, on the other hand, is strictly US-centric and narrower in scope. It specifically protects Protected Health Information (PHI) held by covered entities (healthcare providers, plans, clearinghouses) and their business associates. It doesn’t cover general consumer data unless it’s linked to health services. Violations can result in fines ranging from $100 to $50,000 per violation, with an annual cap of $1.5 million per category.
| Feature | GDPR | HIPAA |
|---|---|---|
| Jurisdiction | EU/EEA residents (global reach) | US healthcare sector |
| Data Scope | All personal data (PII) | Protected Health Information (PHI) |
| Consent Model | Explicit, granular consent required | Implied consent for treatment/payment |
| Max Penalty | €20M or 4% global revenue | $1.5M annual cap per violation type |
| Training Focus | Data subject rights, lawful basis | Minimum Necessary Rule, PHI safeguards |
Notice the "Training Focus" row. This is where most companies mess up. They train everyone on "data privacy" generally. Instead, split your curriculum. For GDPR-heavy roles, drill down on how to handle a Subject Access Request (SAR) within the one-month deadline. For HIPAA roles, focus heavily on the Minimum Necessary Standard-only accessing the data needed for the specific task at hand.
Building a Role-Based Training Strategy
So, how do you build training that actually works? Start by mapping your workforce against risk profiles. Not everyone needs to be a data protection officer, but everyone needs to know their specific liabilities.
- Executives: Need high-level strategic awareness. Focus on liability, brand reputation, and budget implications of non-compliance. Keep it short-30 minutes max.
- IT & Security Teams: Require technical deep dives. Encryption standards, secure disposal methods, and incident response protocols. This should be hands-on, maybe even using sandbox environments.
- Customer-Facing Staff: These are your highest risk group. They interact directly with data subjects. Train them on verbal disclosure rules, how to verify identity before sharing info, and recognizing phishing attempts targeting client data.
- HR Departments: Handle sensitive employee data. Focus on retention policies and internal transfer regulations, especially if you operate across borders.
A common pitfall is assuming that once is enough. Regulations change. In 2026, we’ve seen shifts in cross-border data transfer mechanisms post-Brexit adjustments and updated EU-US data frameworks. Annual refresher courses are mandatory, but quarterly micro-learning sessions-five-minute quizzes sent via Slack or Teams-are far more effective at keeping knowledge fresh.
The Human Factor: Why Culture Beats Compliance
You can have the best software and the strictest policies, but if your culture encourages cutting corners, you’ll fail. I’ve seen companies implement complex multi-factor authentication systems, only for employees to write their passwords on sticky notes attached to monitors. Why? Because the process was too cumbersome.
Effective compliance training isn’t just about teaching rules; it’s about explaining the "why." People follow rules better when they understand the consequences. Show them real examples of breaches caused by human error. Did you know that according to IBM’s Cost of a Data Breach Report, human error accounts for nearly 30% of all breaches? Phishing remains the top entry point for attackers. Training shouldn’t just say "don’t click links." It should show a realistic phishing email example and explain why it looks legitimate.
Encourage reporting without fear. If an employee accidentally sends an email to the wrong recipient, do they hide it or report it? A blame-free culture ensures early detection. Make reporting easy-one-click button in the email client. Reward proactive behavior. Did someone spot a suspicious attachment? Publicly acknowledge them. Positive reinforcement builds habits faster than fear of punishment.
Leveraging Technology for Continuous Learning
Gone are the days of sitting in a dark room watching PowerPoint slides. Modern compliance tools integrate directly into your workflow. Imagine receiving a simulated phishing email on Tuesday morning. If you click it, you immediately get a pop-up mini-lesson explaining what red flags you missed. No waiting for next month’s training session. Immediate feedback loops reinforce learning instantly.
Look for platforms that offer adaptive learning. If an employee consistently passes quizzes on password security but struggles with data classification questions, the system should automatically serve them more content on classification. This personalized approach respects their time and addresses actual knowledge gaps rather than forcing them through material they already know.
Also, consider mobile-first design. Your field sales team or remote developers might not sit at a desk all day. Allowing them to complete five-minute modules on their phones during a commute increases completion rates dramatically. Accessibility matters-if your team can’t easily access the training, they won’t engage with it.
Auditing and Proof of Competence
When regulators come calling, they don’t just want to see attendance logs. They want proof of competence. Can you demonstrate that your staff understands the risks? Design assessments that test application, not just memory. Instead of asking "What does GDPR stand for?", ask "A customer requests deletion of their account. What steps must you take before confirming deletion?"
Maintain detailed records of training completions, scores, and remedial actions taken. If someone fails a quiz, track when they retook it and passed. This audit trail is vital during investigations. It shows due diligence. Even if a breach occurs, proving you had robust training programs can mitigate fines. Regulators look favorably on organizations that invest in prevention.
Finally, review your training effectiveness annually. Are incidents decreasing? Are phishing simulation click rates dropping? Use metrics to refine your program. If click-through rates remain high despite training, the issue isn’t lack of information-it’s likely poor interface design or cultural resistance. Adjust accordingly.
Do small businesses really need formal compliance training?
Yes, absolutely. Size doesn’t exempt you from GDPR or HIPAA obligations. Small businesses are often targeted because they assume they’re too insignificant to bother with. Formal training provides documented evidence of due diligence, which can significantly reduce potential fines if a breach occurs. Even a basic, well-documented annual workshop is better than no training at all.
How often should compliance training be refreshed?
Annual comprehensive training is standard, but quarterly micro-learning sessions are recommended for high-risk roles. Regulatory landscapes change frequently, and human memory fades quickly. Short, frequent touchpoints keep critical concepts top-of-mind better than one long annual session.
Can online training fully replace in-person workshops?
For most general staff, yes. Online platforms offer scalability and consistency. However, for specialized roles like Data Protection Officers or IT security leads, in-person or virtual live workshops allow for deeper discussion of complex scenarios and Q&A opportunities that pre-recorded videos cannot match.
What is the biggest mistake companies make in compliance training?
Treating it as a one-time checkbox activity rather than an ongoing cultural initiative. Many companies focus solely on passing audits rather than fostering genuine understanding. This leads to low engagement, poor retention, and ultimately, higher risk of human-error breaches.
Does GDPR apply to companies outside the EU?
Yes. GDPR has extraterritorial scope. If your company offers goods or services to individuals in the EU, or monitors their behavior (like tracking cookies), you must comply with GDPR regardless of where your headquarters are located.
